By Raj Brar, Founder of Argus AI Labs
The Limits of Data Residency as a Sovereignty Strategy
A workload can keep every byte inside an approved jurisdiction and still leave the enterprise without meaningful control. Model updates may occur outside its approval process. Telemetry may leave the operating boundary. Encryption keys, identity policies, or runtime evidence may remain under another party’s authority. The data is resident, but the intelligence system is not sovereign.
For enterprise architects and data-platform leaders, the decisive question is not simply where data sits. It is whether the organization controls the chain of decisions that turns that data into action. Sovereign intelligence is an operating architecture for control across data, identity, models, inference, infrastructure, keys, and audit evidence—not a vendor label or compliance checkbox.
The Control Planes Behind Sovereign Intelligence
Treat sovereignty as a set of discrete control planes rather than a single property. Each plane represents a distinct locus where authority can be exercised—or lost. A robust sovereign intelligence architecture coordinates all of them. Missing one undermines the rest.
The six control planes are:
- Data: where data is stored, how it moves, and who can access it through every lifecycle stage
- Identity: who and what can authenticate, with what privileges, under what conditions
- Model provenance: which model is in use, where it came from, and who authorizes changes
- Inference infrastructure: the compute, networking, and telemetry that execute model runs
- Key ownership: who holds encryption keys and who can revoke access
- Audit evidence: what is logged, who can verify it, and what cannot be altered
This framework forces each dependency into the open. If the organization cannot identify who authorized the last model update, what changed, and what evidence proves it, that plane remains delegated rather than controlled.
Data and Identity Boundaries
Data sovereignty requires more than geographic placement. It requires control over the entire lifecycle: ingestion, transformation, storage, retrieval, retention, and deletion. The architecture must also identify which operational telemetry may cross the boundary. Usage records, error logs, prompts, outputs, and performance traces can reveal sensitive information even when the underlying database never moves.
Identity and authorization boundaries are equally critical. Your organization must control not only who accesses the AI system but also what those identities can do at the model, API, and infrastructure layers. Service accounts, cross-tenant permissions, and inherited IAM roles are common sources of privilege leakage. When a vendor manages your identity layer, you inherit their decisions about who can impersonate, escalate, or bypass governance controls.
Design for identity at two levels. First, the data plane identity for human and application users interacting with the AI service. Second, the control plane identity that governs who can change configuration, update models, or access encrypted storage. The second is frequently overlooked and frequently outsourced to the vendor.
Model Provenance and Update Authority
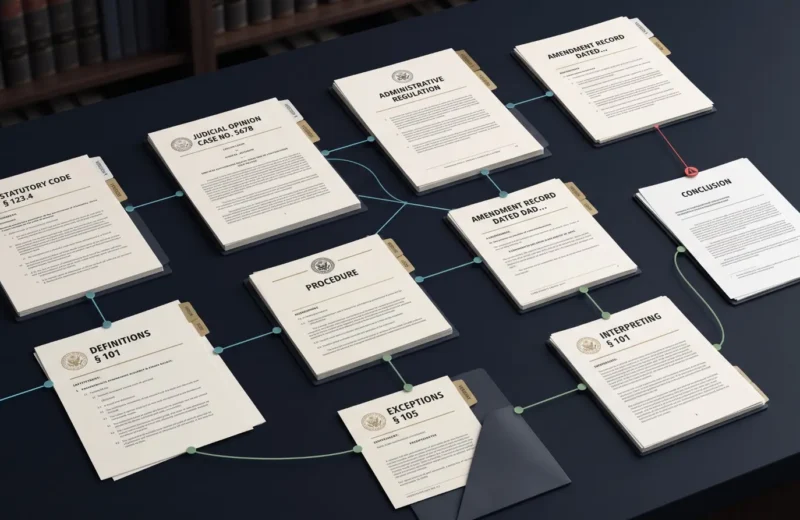
A sovereign intelligence system must account for model provenance. Which model is running? Where was it trained? Who owns its weights? More importantly, who decides when the model is upgraded, fine-tuned, or replaced?
Open-weight and proprietary models create different control problems. An open-weight model gives the organization custody of an artifact, but custody is not governance. Without a registry, signed versions, evaluation records, promotion controls, and rollback discipline, teams can run different weights under the same model name and still have no defensible answer about what produced an output.
A proprietary API delegates more of the stack, but a strong service agreement, fixed-version access, change notices, evaluation gates, and retained audit evidence can provide clearer operating control than an unmanaged open-weight deployment. Sovereignty therefore cannot be reduced to “open” versus “closed.” The real test is whether model identity, change authority, evaluation, and rollback are explicit and enforceable.
Most production environments also route work across multiple models or providers. That multiplies the governance surface: each route needs an approved purpose, data boundary, model version, fallback rule, and evidence trail. The registry must record not only which models exist, but which policy selected a model for a particular request.
Inference Infrastructure, Telemetry, and Key Ownership
Inference infrastructure is where sovereign claims often collapse. Residency tells you where compute physically sits, but not who controls it. Managed inference services hide resource allocation, scheduling, and telemetry behind provider APIs. Your organization cannot inspect the runtime, cannot verify that only approved workloads are executing, and cannot independently confirm that inference outputs are not cached or logged by the provider.
Telemetry deserves special scrutiny because operational logs, model inputs, and outputs may be handled separately from primary data. The appropriate control may be self-hosted inference, a dedicated private environment, or a governed managed service with enforceable retention terms and organization-controlled evidence. The architectural requirement is verifiability: the enterprise must know what is captured, where it goes, how long it persists, and how access can be revoked.
Key ownership follows the same logic. If the provider holds your encryption keys—or manages the key escrow system—then the provider can access your data, models, and inference history. Sovereign intelligence requires that your organization control key generation, storage, rotation, and revocation. This is a technical requirement, not just a compliance artifact. Hold the keys and you can enforce access; lose them and you have delegated authority to a third party whose incentives may not align with yours over time.
Auditability Failure Modes and Trade-offs
Auditability fails in predictable ways. Logs are incomplete, timestamps are unreliable, and log storage is controlled by the same party that produced the events. If your audit trail depends entirely on the vendor’s telemetry, a dispute about what happened in the system is decided by the vendor’s records. That is not an audit trail—it is a courtesy log.
Sovereign intelligence requires an independent audit surface. This means logs that your organization ingests, stores, and controls. It means evidence of model versions, access decisions, and infrastructure changes that cannot be altered retroactively. It means being able to answer the question, “What exactly executed here, with which model, at what time, under whose authorization?” without relying on a third party’s self-report.
Auditability also creates real design trade-offs. Consider a hypothetical claims workflow that records every prompt, retrieved document, model response, and reviewer action. That produces strong reconstruction evidence, but it may also copy sensitive material into a second system and extend its retention period. Logging less protects privacy but weakens investigation. The answer is not “log everything.” It is to classify the evidence required for each workflow, minimize sensitive payloads, separate security logs from content records, and set retention according to operational and legal need.
A Phased Reference Architecture for Sovereign Intelligence
There is no single sovereign architecture for every organization, but a phased approach helps sequence decisions in order of risk. Start with the highest-risk control planes, then expand as operational maturity grows.
Phase 1: Control the data plane. Move all sensitive data ingestion, transformation, and storage under your organization’s own infrastructure controls. Enforce encryption at rest and in transit with keys your organization manages. Verify that no telemetry leaves your environment without explicit, documented consent.
Phase 2: Control identity. Integrate the AI system with your organization’s existing identity provider. Remove default service accounts and cross-tenant permissions. Define separate roles for model administrators, inference operators, and auditors.
Phase 3: Control the model registry. Stand up a model registry that supports versioning, signing, promotion workflows, and rollbacks. Establish an owner for every model in production. Document the approval chain for every update.
Phase 4: Control inference infrastructure. Move inference to hardware and networking that your organization can inspect. If using a managed offering, require contractual access to runtime logs and infrastructure metadata. Where possible, use attestation to verify the execution environment.
Phase 5: Control the audit surface. Ingest all critical logs into your own storage. Build reports that tie model versions, access events, and infrastructure changes together. Test restoration of the audit trail periodically.
This sequence allows an organization to make progress on sovereignty without a forklift replacement of its entire AI stack. Each phase closes a specific control gap and creates evidence for procurement decisions down the line.
What We Learned Building Governed Intelligence Systems
I came to sovereign intelligence through diagnostics, not vendor marketing. I began working with complex automotive systems in 1991, where I learned that a system can look healthy while control is fragmented across components nobody owns end to end. At Argus AI Labs, that lesson shapes how we connect source control, identity, provenance, governed retrieval, workflow authorization, infrastructure boundaries, and evidence. The language model is an interface inside that system—not the intelligence system itself.
The practical lesson is that every abstraction layer transfers some authority. That transfer may be entirely reasonable, but it should be explicit, bounded, and reversible. The objective is not to eliminate managed services. It is to preserve organizational control over the knowledge, policies, models, and evidence that determine how intelligence is produced and used.
The Sovereignty Standard That Works
Define a concrete standard for your organization. It should cover residency, access, model provenance, infrastructure control, and auditability—in writing, with named owners for each. Use this standard to evaluate every AI procurement. When a vendor cannot answer where model updates originate, who holds keys, or what telemetry leaves the environment, treat that as a material gap.
Sovereign intelligence is not a product you buy. It is an architecture you operate. The distinction is the difference between control and compliant dependence.
Score all six control planes. For each one, document who holds authority today, what can be changed without your approval, what evidence your organization retains, and whether control can be revoked or transferred. Ambiguity is itself a finding: it identifies where procurement language has not yet become operating control.
Frequently Asked Questions
What is sovereign intelligence?
Sovereign intelligence is an operating architecture that keeps meaningful authority over enterprise data, identity, models, inference, encryption keys, and audit evidence within boundaries the organization defines and can verify. It is not the same as owning every component; it means delegated services remain governed, observable, and reversible.
How is sovereign intelligence different from data residency?
Data residency answers where information is stored or processed. Sovereign intelligence asks who can access it, which model can use it, who authorizes changes, what telemetry leaves the environment, who controls encryption keys, and whether the organization can reconstruct what happened. Residency is one control plane, not the complete architecture.
What should enterprises evaluate in a sovereign intelligence architecture?
Evaluate six control planes: data lifecycle, identity and authorization, model provenance, inference infrastructure, key ownership, and audit evidence. For each plane, identify the current authority holder, the change and revocation process, the retained evidence, and the consequences if a provider or model is replaced.